I get you into cybersecurity the fast way.
Writing functional specs for a stock management system, watching the clock, going home. I had one thing going for me: a very specific picture of where I wanted to end up. Freelance cybersecurity expert and owner of a cybersecurity business with serious clients on the books.
It took three years, and nobody handed me anything. I made most of the mistakes listed further down this page, which is exactly why I can name them.
I got into the industry through consulting: IT financial audit, compliance for internal control, forensic investigation, pentesting, security analysis. Then I moved inside, as a security architect.
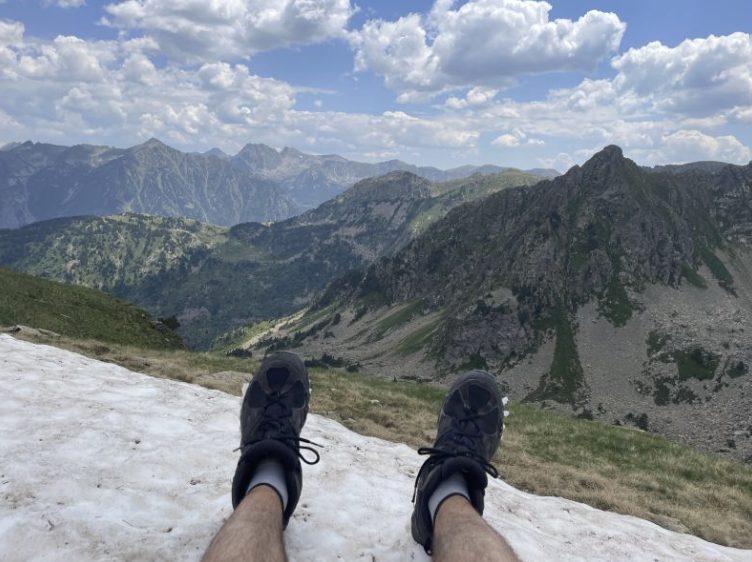
Fifteen years of cybersecurity later, seven of them designing security for international retail groups across five continents, I teach the Web Security by Design module at Paris 1 Panthéon-Sorbonne and I build dmarc-expert.com, an email security SaaS used by large companies. That's the picture I had in my head at the start, made real. I also wanted to be able to work from anywhere, and that part is real too: I work remotely from the Pyrenees, up in the mountains on the border between France and Spain.
And I enjoy it. The subjects never repeat, and the work is a cat and mouse game with the attackers: there is excitement, there is fear, and there are real wins. You talk to everyone, from the CEO to the CFO, from the CTO to the engineers, from the business to the clients and the suppliers. You never feel isolated, and you never feel stuck.
I'm handing you the process and the knowledge I would have loved to have when I started.
Expert level in far less time, without the wasted years and without burning yourself out.
None of that means you're too late.
It means nobody has sat down with you and drawn the map.
You've been told security is sealed off. That it takes a degree, a clean computer science record, and years of IT behind you before anyone returns your call.
Look at who actually does this work. Very few of them started here. They came from support desks, from development, from system administration, from law, from accounting, from investigation, from teaching, from the army, from sales. Plenty came from outside IT entirely.
That isn't an accident. Security is the one part of technology that touches every floor of a business, so it needs people who already know those floors. It is multidisciplinary by nature, and it hires that way.
Which means the years you spent somewhere else are not a hole in your CV. A good part of what you already know is exactly what this work runs on:
None of that is a consolation prize.
It's a head start, and most of the people carrying it have no idea it counts.
The jump is smaller than you think. What's missing is the order to do things in, and someone who has already made it sitting next to you. That's the whole job of this coaching, and the point is to get you across fast.
Your background, your money, your time, the people around you. No plan survives if it ignores the life you actually have.
If you already know, we aim. If you don't, I walk you through the specialities: what the work is really like day to day, what it pays, who gets in, and what it costs you to get there.
Nobody starts from zero. Your technical background, your industry knowledge, your languages, your patience with people, the way you hold up under pressure. Security needs all of it.
Technical work, how this industry actually behaves, your CV, your LinkedIn, and interview preparation. So you don't lose a role you deserved over three small avoidable mistakes.
This coaching is built for getting into the industry. If you already have at least seven years of IT experience, you don't need to get in. You need to move up. The technical background is already there, what is missing is the method.
That is what the security architect program does: four weeks, on your own projects. It is the royal road of this profession, the one that leads to the very top salaries in cybersecurity and to the roles where you can ask for full remote. You can take it on your own.
See the security architect program →
A few lines is enough: what you do now, what you'd like to do, and how much time you honestly have. I'll study it and come back with what I think you should do.
Tell me where you are →